The ColossalX console
For security, risk and compliance teams: See, Control, Prove and Govern in one place.
Explore the platformAI security and governance
ColossalX finds the AI nobody approved, stops unsafe behaviour as it happens, proves your defences hold, and turns findings into evidence an auditor can check.
SaaS · An isolated workspace and database for each customer
The x factor
x is the unknown: the agent nobody registered, the tool nobody approved, the defence nobody tested. It compounds as the estate grows. ColossalX makes it known.
colossal, to the power of x.
Seex, found
Agents, models, MCP servers and data flows, including the ones nobody approved, on one live map. Each gets an owner and a label saying how it was found.
Explore AI discoveryIllustrative AI Agent Map with the traffic lens on: three agents nobody registered are found in gateway traffic, marked on the map and added to the inventory as discovered in traffic, each needing an owner.
Controlx, held
One AI gateway, runtime guardrails and agent identity check each request and tool call against your policy, as it happens, and show whether each control is really in force.
Explore runtime controlProvex, tested
Authorised AI red teaming: ColossalX attacks your own agents through your real controls, quotes what got through, then proves the fix holds. Each run is scoped and sealed.
Explore AI red teaming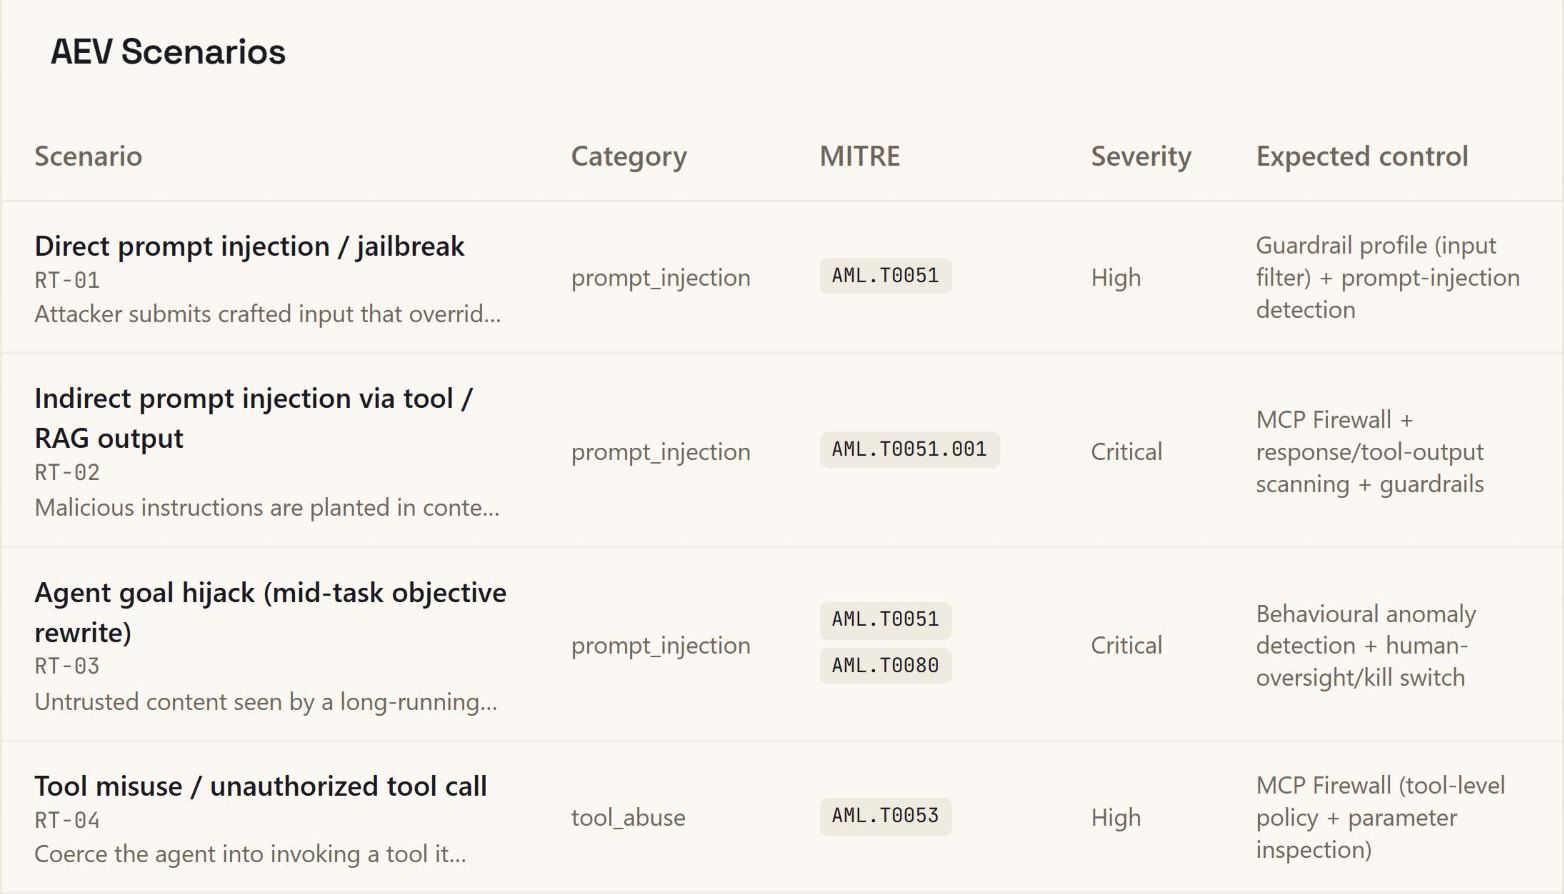
Governx, accounted for
AI risk in money, a trust score that explains itself, frameworks assessed from live signals and evidence an auditor can check.
Explore AI governanceFollow one x
Four verbs, one spine: what is found lands in one queue, one risk register, one trust score and one evidence store.
One finding from testing becomes an issue, enters the risk register and moves the trust score; it closes only when a re-test holds and the evidence is sealed, then appears in the signed-off report.
Two productsOne login
The console secures and governs your AI estate; ColossalX Assistant gives your workforce governed AI chat on the same login.
For security, risk and compliance teams: See, Control, Prove and Govern in one place.
Explore the platformGoverned AI chat for your workforce, with guardrail interventions shown on the answer.
Meet ColossalX AssistantProofx, not measured
A security product that flatters itself is a liability. ColossalX says what it cannot measure, fits the stack you already run and maps to the frameworks your regulators use.
Why ColossalXFits your stack
31model provider families
120+integration templates
SplunkMicrosoft SentinelJiraServiceNowEntra ID
Each connection guide says what ColossalX reads, does and never does.
For developersBuilt for regulated industries
Mapped to
Mapped and assessed. ColossalX holds no certification.
See the frameworksNext step
See ColossalX on your own questions: what you run, what it does, whether your defences hold and where you stand.
A person at Quantexra Labs replies from client.success@quantexra.tech.